API Development Sydney Australia
Connect your website, software and business tools with APIs built for reliable data sharing.
Connect your website, software and business tools with APIs built for reliable data sharing.
Product and engineering leaders who need reliable interfaces between systems or for external consumers.

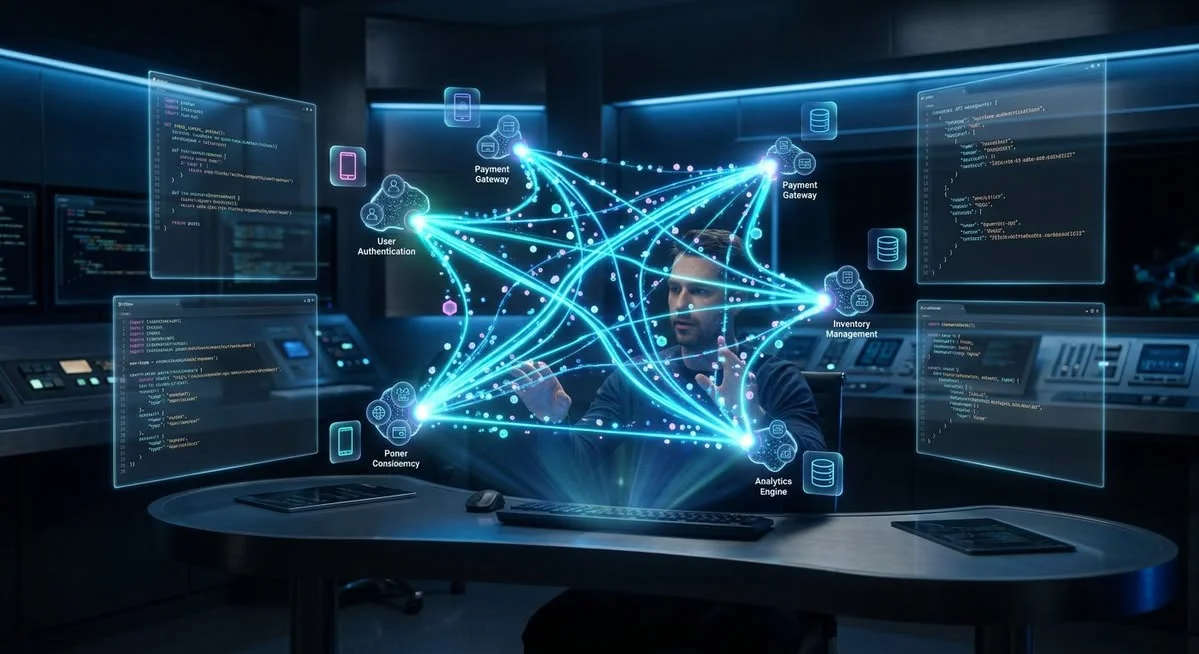
Consumers, use cases and data ownership are mapped into a proposed API contract before coding deep.
Authentication, authorisation and abuse protections are designed into the service.
Endpoints ship with docs and examples so integrators can move without Slack archaeology.
Partner or client apps validate against a sandbox; we fix friction before production cutover.
Technologies We Use
The right tools for your project. We choose technologies that suit your goals, budget and ongoing support needs.
Architecture3 tools
-
REST API Standard HTTP API design for broad compatibility
-
GraphQL Flexible query language for efficient data fetching
-
WebSockets Real-time bi-directional communication


Runtime3 tools
-
Node.js High-throughput event-driven API server
-
Python / FastAPI High-performance async API with auto docs
-
Laravel Full-featured PHP framework for API backends


Database2 tools
-
PostgreSQL ACID-compliant relational database
-
MongoDB Flexible document store for unstructured data


Caching1 tool
-
Redis In-memory cache for rate limiting and sessions

Security1 tool
-
JWT / OAuth2 Industry-standard token-based authentication

Docs1 tool
-
Swagger / OpenAPI Auto-generated interactive API documentation

Cloud1 tool
-
AWS Lambda Serverless functions for scalable API endpoints

DevOps1 tool
-
Docker Containerised deploys for consistent environments

Testing1 tool
-
Postman API testing, mocking and documentation

Simple, clear api development for your business.
Explore our projects to see how we turn business goals into practical results.
-
 Web & Experience Trend Beacon How Techable Australia helped Trend Beacon sharpen positioning and accelerate growth. Read case study
-
 Growth Marketing Market Motion How Techable Australia helped Market Motion sharpen positioning and accelerate growth. Read case study
-
 Brand Strategy Tidal Strategy How Techable Australia helped Tidal Strategy sharpen positioning and accelerate growth. Read case study
-
 Digital Marketing Growth Engine How Techable Australia helped Growth Engine sharpen positioning and accelerate growth. Read case study
-
 Brand Strategy Market Magnet How Techable Australia helped Market Magnet sharpen positioning and accelerate growth. Read case study
Why teams trust us with API Development
- 01
Clear agreements between systems
We define endpoints, data formats and expected responses before implementation. This gives your teams and integration partners a shared understanding of how the API works.
- 02
Access controls built into the plan
We plan authentication, permissions and input validation around your data and users. Rate limits and error handling help manage how connected applications use the API.
- 03
Integrations tested end to end
We check normal requests, invalid inputs and service failures, alongside the connected workflows. Performance checks and monitoring help prepare the API for expected usage.
- 04
Documentation that supports future changes
We provide practical usage examples and document the API behaviour. Versioning and handover guidance help your team extend integrations while managing changes for existing users.
Questions about API Development
What is an API and why would our business need one?
An API lets software systems exchange data through defined requests. It can connect a website, app or internal tool without repeated manual entry. A clear integration need is the starting point for deciding whether API development is worthwhile.
Can you integrate an existing API instead of building a new one?
If a suitable API already exists, integration may be the simpler option. We review its capabilities, access requirements and limits. A custom API is useful when your system needs to expose data or functions that are not available otherwise.
What is included in API development?
The scope can cover data models, endpoints, authentication, validation and documentation. Testing and deployment requirements should be specified too. We agree what other systems need from the API before implementing it.
How do you secure an API?
Controls depend on the data and users involved. Authentication, permissions, input checks and secure credential handling are common foundations. We define the relevant risks during scoping and test access boundaries before release.
What if the third-party system has API limits?
Rate limits, access plans and missing features can affect the integration. We review those restrictions early and plan appropriate scheduling or error handling. A connection should not assume unlimited requests or capabilities the provider does not offer.
How do you keep data consistent between connected systems?
We define which system is the source of truth and how updates, duplicates and conflicts are handled. The sync schedule should match the business need. Logs and recovery steps help resolve incomplete transfers.
Will we receive API documentation for our developers?
Documentation should describe endpoints, authentication, expected data and errors. Example requests make handover easier. We agree the documentation and access your team needs so future developers can work with the API confidently.
What determines API development and integration cost?
Cost depends on endpoints, data complexity, provider limitations and testing needs. Monitoring and future provider changes may require ongoing support. Reviewing third-party documentation first helps produce a realistic estimate.
Talk to us about API Development
Bring the brief, the budget or just the problem. You will get a straight answer on scope, timing and whether this is the right service for it.